
Your always-on security team, run by AI agents.
CyberSpec's agents watch every domain, IP and range you have verified, explain each vulnerability and its fix in plain English, and tell you within a day, so you can fix it before it is exploited. £15 per client a month, no contract.
Preparing clients for Cyber Essentials? See which ones would likely fail the CE+ external scan, before the assessor does. See a sample readiness report.
- Free plan, no card
- Buy online, no sales call
- AI is labelled, and a human decides
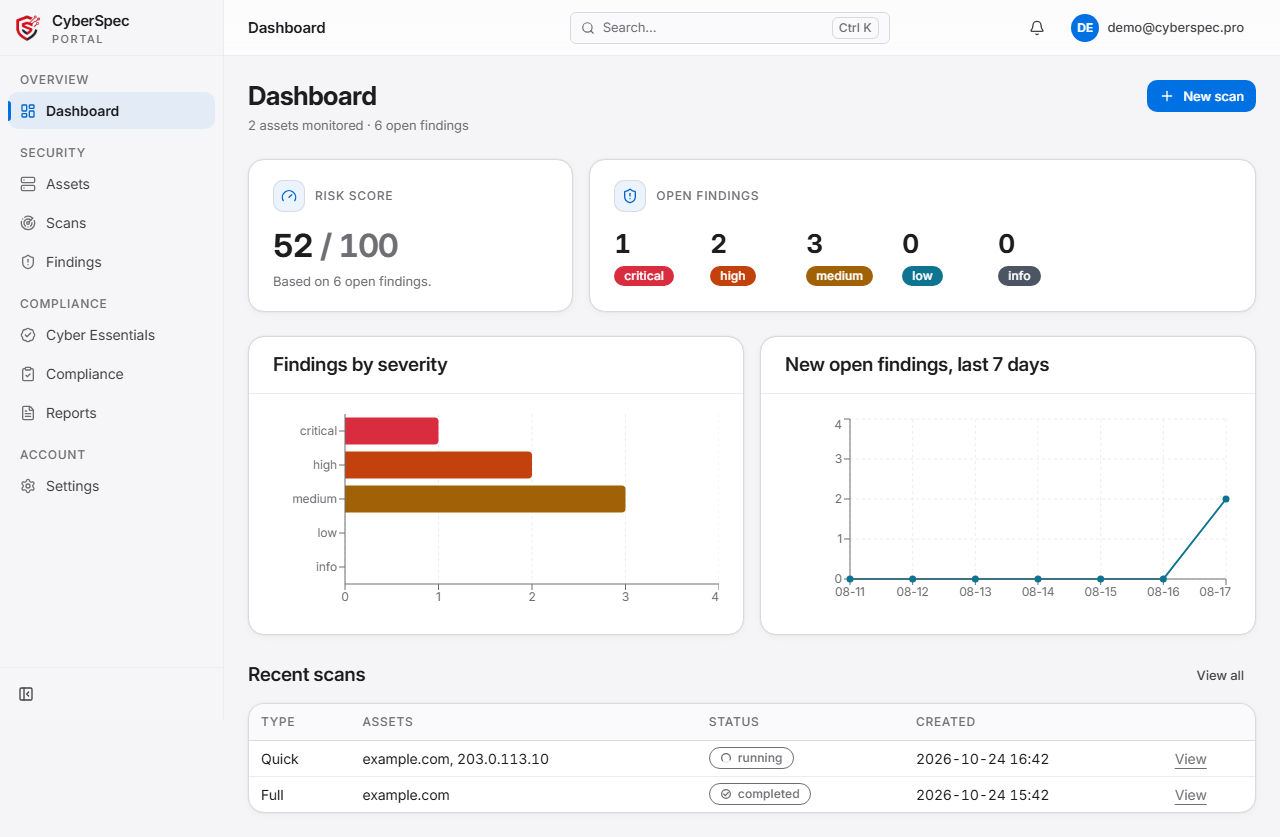
Explain · AI
Every finding, explained in plain English
Open a finding and the Explain agent writes what it is and how to fix it. The text is labelled as AI and sits under the scanner's own facts.
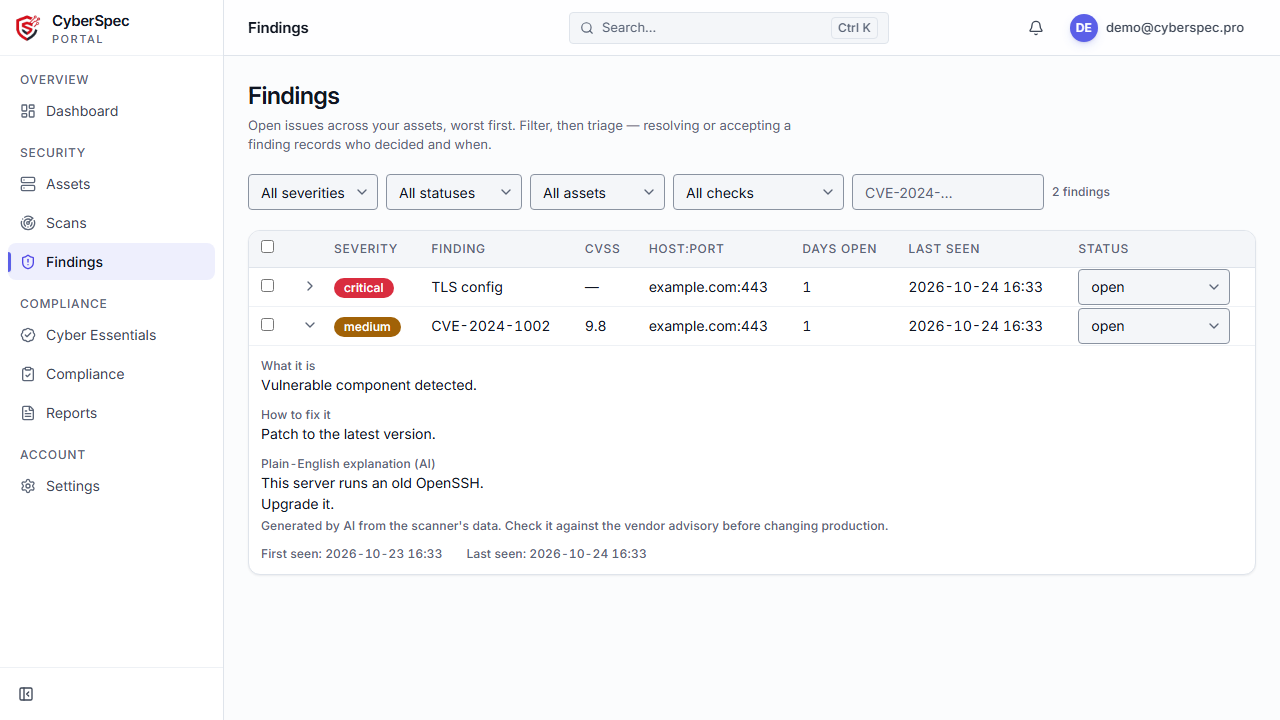
Cyber Essentials readiness
Know what an assessor would find
Each of the five controls is read against your latest scan as likely fail, review or no issues found, with a list of what a scan cannot see.
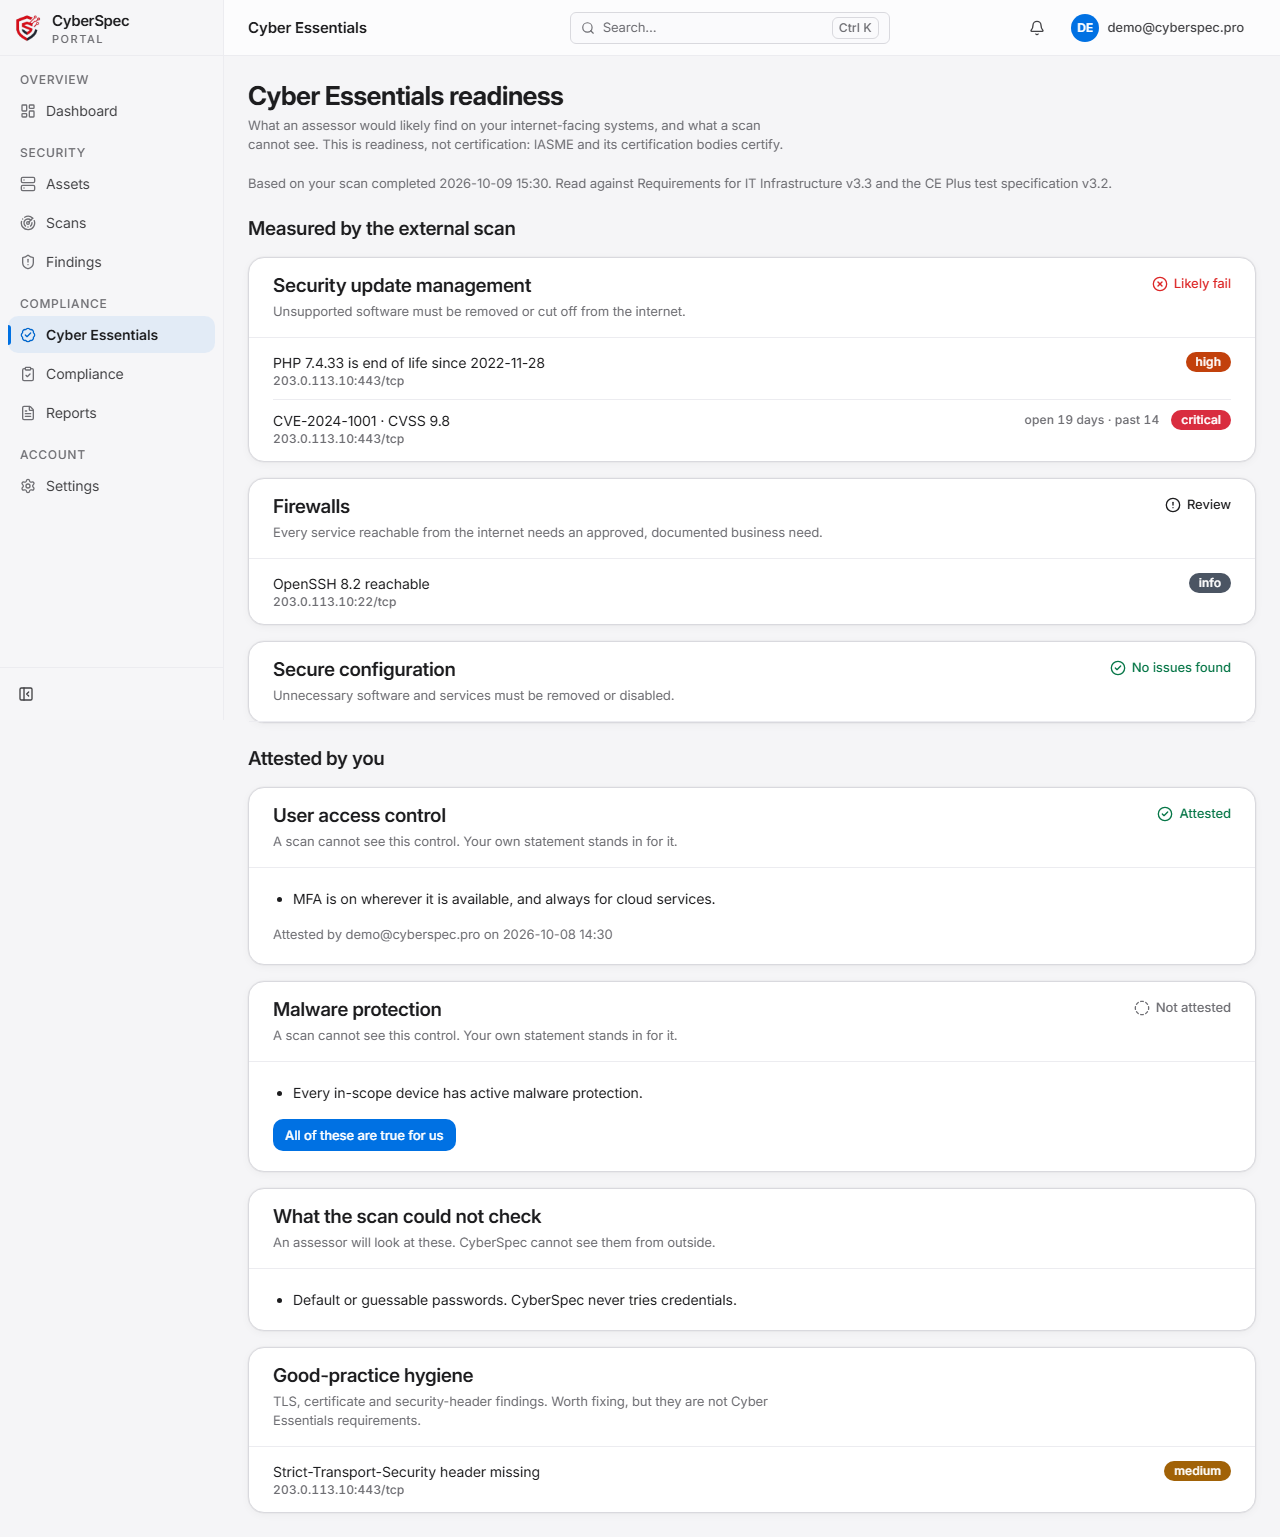
£15
Per client per month. The scanners this replaces open at five figures and a sales call.
£0
Free plan: one asset, no card, no trial clock.
6
Agents live today. Each one is marked AI or automation, so you know which is which.
The AI-era exposure window
Attackers are using AI to turn fresh patches into working exploits faster.
- Exploited flaws disclosed in 2026, by August
- 141
- against 127 in the whole of 2025 (Google Threat Intelligence Group)
- From a published fix to exploitation
- 4 days
- for one 2026 BeyondTrust flaw, with five more groups within a week (GTIG)
A yearly scan can't keep pace with that, and neither can a team without security staff. So CyberSpec answers with agents: Scout re-checks what you expose on schedule, Explain turns each new finding into a fix you can act on, and Digest makes sure someone hears about it within a day.
What the 2026 data shows, and what it doesn'tScanners don't map compliance. Compliance tools don't scan.
Enterprise scanners find exposure and sell it through a sales call and a five-figure contract. Compliance platforms collect evidence for an audit. Neither answers the question an MSP asks before a client's Cyber Essentials assessment, or a team asks before a SOC 2 audit: which control does this open finding break?
CyberSpec answers it on every finding on the MSP plan, without a sales call.
CVE-2022-3602
203.0.113.42:443
OpenSSL 3.0.0–3.0.6 X.509 name-constraint buffer overflow — upgrade to 3.0.7 or later.
maps to SOC 2 CC7.1 · ISO 27001 A.8.8
Meet the agents
6 agents work today. Each is marked AI or scheduled automation, so you can decide how far to trust it.
Scout
AutomationWatches your attack surface
Re-scans every verified domain, IP and range on the schedule you set, and names the software it finds (WordPress, Next.js, PHP) with its version.
- Scheduled and on-demand scans of verified assets only
- Framework and CMS detection with version where exposed
- End-of-life and outdated-version checks against endoflife.date
Explain
AITurns findings into fixes
Writes what each finding means, why it matters and how to fix it, in plain English. It uses only the scanner's own facts and is labelled as AI.
- One-click plain-English explanation on every finding
- Grounded in the CVE, product, version and severity the scan recorded
- Points you back to the vendor advisory to check it
Brief
AIWrites the report for leadership
Drafts the executive summary at the top of every PDF report, so the person who signs off reads a page, not a findings table.
- AI-written executive summary in PDF reports
- Falls back to a findings-only report if the AI is unavailable
- Never claims certified, compliant or pass
Digest
AutomationTells you within a day
One email a day to the account's owners, only when something is new: each new issue with how to fix it, and newly detected software.
- Daily digest, on by default, silent when nothing changed
- Email alerts on new critical and high findings
- Slack and webhook alert rules for your own tooling
Triage
AIDecides what to fix first
Puts anything on CISA's known-exploited list at the top of your fix order, then suggests what to do with each finding and why, for a person to accept.
- Fix order led by CISA's known-exploited list, not CVSS alone
- Suggested next step (fix, accept risk, false positive) with its reasoning
- Nothing changes until a person accepts it
Code
AutomationChecks the code you ship
Connect a codebase with one command from the @cyberspec/sdk package. Your dependencies are checked against known vulnerabilities, and the findings and fixes land next to your scan results.
- Reads lockfiles for npm, Python, Go, Rust, Ruby, PHP, Java and .NET on your machine
- Sends package names and versions only, never your source
- Upgrade-to version for every vulnerable package; AI source review is on the roadmap with the Validate & Fix add-on
Being built nextROADMAP
- Validate — Checks whether a finding can actually be exploited on your system, with evidence, so you fix what is real first. Uses OpenAI cyber models, inside a scope you sign.
- Remediate — Turns a finding into a ready-to-review fix: a config change, an upgrade step or a ticket, written for your stack.
- Inside — A lightweight agent on your own machines that checks what an external scan cannot see: patch levels, admin accounts, firewall and malware protection.
How the agents hand off
- 1
Verify what you own
Domain, IP or CIDR range, by DNS TXT record, well-known file or attestation.
- 2
Scout watches
Scheduled scans, software and version detection, end-of-life checks.
- 3
Explain writes the fix
Plain English, built from the scan’s own facts, labelled as AI.
- 4
Digest and Brief report
Owners hear within a day; leadership gets the summary.
AI you can point at production
Built from the scan
Explain works from what the scanner recorded: the CVE, product, version and severity. Brief summarises the report's findings. Neither one creates a finding.
Labelled every time
AI output is marked as AI, sits below the scanner’s own remediation, and points you to the vendor advisory.
A human decides
Agents explain and summarise. Status changes and fixes are yours to make, and no agent changes anything on your systems.
Your assets only
No agent touches anything until ownership is verified and a scanning agreement is accepted, asset by asset.
No certification claims
Agents never say certified, compliant or pass. They report readiness and leave certification to auditors.
Not trained on you
CyberSpec trains no model on your findings. AI calls are capped per account per day, and cached once written.
Two-factor set up at first sign-in, on every account
TOTP setup is the step right after your first sign-in, on every sign-in method. You can skip it and turn it on later. The skip is audit-logged, and our own admin accounts can't skip at all. Backup codes are issued at enrolment, and every active session is visible and revocable from Settings.
How CyberSpec secures your accountSimple pricing
Free
£0
1 asset, on-demand scans.
MSPFor MSPs
£15/client/mo
Up to 5 assets per client, scheduled scans, CE readiness.
CE report
£100 one-off
One readiness scan, readiness view and findings PDF for one client.
Enterprise
Custom
Volume pricing, uncapped assets, SSO/SAML.
Frequently asked questions
How this year's attacks got in
Write-ups of the attacks and vulnerabilities our checks cover: what got exploited, and what to fix first.
· 3 min read
SonicWall CVE-2026-19868: SAML MFA bypass
A SonicOS SSL-VPN flaw lets a valid login for another auth method skip SAML and its MFA. It is in CISA KEV. Affected builds, fixes and what to check.
· 4 min read
WordPress CVE-2026-119977: update-window RCE
A race in WordPress core updates lets an unauthenticated attacker run code mid-upgrade. It is in CISA KEV. Fixed versions, what to check, what to block.
· 4 min read
GitLab CVE-2026-97229: CI regex RCE, now in KEV
A CVSS 10 flaw in GitLab's CI/CD regex compiler is now actively exploited. Which self-managed versions are affected, what to patch, and what to lock down.